How to Protect Business Files When Using Cloud Storage
Effectively protecting Business Files When Using Cloud Storage requires more than just picking a reputable provider. Many companies migrate their workflows to the cloud for convenience, yet they often overlook the specific configuration steps needed to ensure their data remains private.
You can maintain a high level of security by implementing a multi-layered approach that addresses both account access and the way you share information. This article provides the actionable strategies you need to keep your company’s digital assets safe from unauthorized eyes while maintaining the flexibility your team requires to stay productive.
Immediate Steps for Account Security
The most critical action you can take is enabling multi-factor authentication (MFA) on every account. Without this, a single compromised password is all an attacker needs to gain full access to your company’s entire repository of files. MFA adds a secondary layer, such as a time-sensitive code sent to your mobile device or a physical security key, which makes stolen credentials largely useless to unauthorized parties.
Implementing Strong Authentication Policies
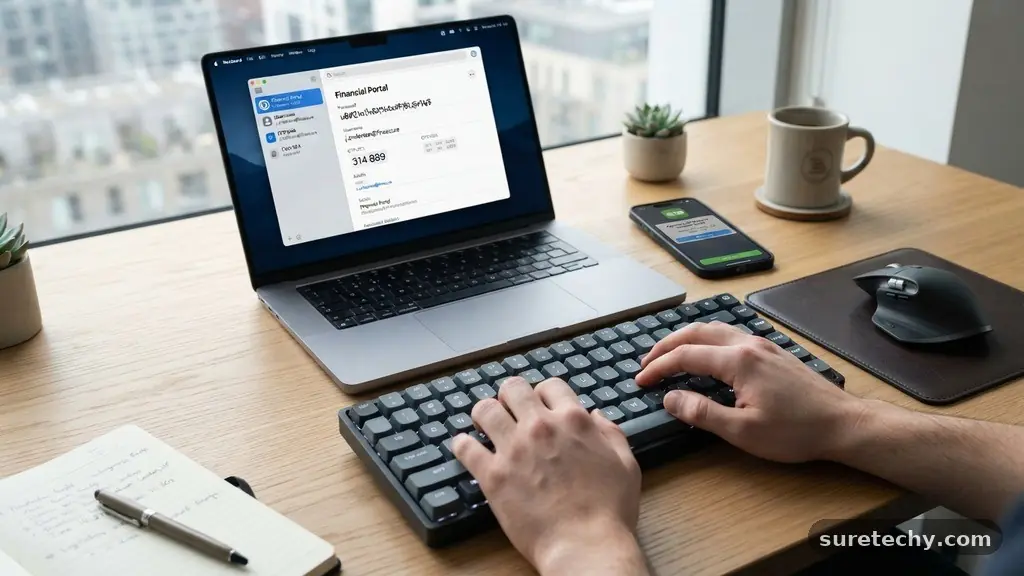
You should mandate that every team member uses a unique, complex password generated by a reliable manager rather than repeating credentials across platforms. This prevents a breach on a less secure site from rippling into your business storage.
Most enterprise cloud providers offer administrative controls to enforce these password requirements across your entire organization. Do not allow your team to bypass these settings, even for convenience.
Understanding Encryption Standards
Encryption acts as your final line of defense if an unauthorized party manages to bypass your network perimeter. Most professional cloud services use AES-256 encryption for data at rest, which is the industry standard for securing sensitive business documents.
You should confirm that your chosen provider supports “zero-knowledge” encryption if you handle highly confidential records. This means the service provider cannot access your files because they do not hold the decryption keys.
Data in Transit vs. Data at Rest
Data is most vulnerable when it moves from your local device to the server. Ensure your provider uses TLS 1.2 or higher to secure your connection, which prevents “man-in-the-middle” attacks from intercepting your files during uploads.
You can verify this by checking for the padlock icon in your browser when accessing your files. If you are using a desktop client, ensure it is configured to use secure protocols exclusively.
Managing Access Permissions Effectively
The principle of least privilege is essential for protecting Business Files When Using Cloud Storage. You should grant team members access only to the specific folders and documents required for their current tasks.
Avoid the common mistake of sharing entire drive roots with broad groups of employees. When someone leaves your company, their access should be revoked immediately, not just at the end of the week.
Refining Link Sharing Habits
Sharing files via public links is a major security risk that often leads to data leaks. If you must use a link to provide access, always set an expiration date and, if possible, require a password for the recipient.
Never leave files shared with “anyone with the link” enabled for long-term projects. Use the granular sharing features provided by services like the Cybersecurity and Infrastructure Security Agency to track who has viewed or edited a document.
Comparing Common Cloud Security Features
Different providers offer varying levels of protection, so understanding what is included in your subscription is vital. While basic tiers often lack advanced auditing tools, business-grade subscriptions typically include detailed logs that show exactly who accessed a file and when. Use this data to spot unusual patterns, such as a large-scale download occurring at 3:00 AM from an unfamiliar IP address.
| Feature | Basic Account | Enterprise Account |
|---|---|---|
| MFA Support | Standard | Enforced/Mandatory |
| Audit Logs | Limited | Comprehensive/Real-time |
| File Recovery | 30 Days | 365 Days+ |
| Data Loss Prevention | None | Automated Scanning |
Avoiding Risky File Types
Some file types are inherently more dangerous to store in the cloud because they can execute malicious code if opened. You should avoid uploading executable files, scripts, or macros that could trigger a malware infection on any device that syncs with your storage. Instead, use compressed formats like ZIP files with password protection if you need to transfer complex data packages.
The Dangers of Syncing
Syncing your entire local drive to a cloud service can be risky if your computer is infected with ransomware. If a malicious program encrypts your files locally, that encrypted version will immediately sync to the cloud, overwriting your clean backups.
To protect against this, maintain an offline, air-gapped backup of your most important business records. You should also use cloud services that support “versioning,” allowing you to restore a previous, uninfected state of a document.
Device Management and Endpoint Security
Your cloud storage is only as secure as the device used to access it. If an employee uses a personal laptop with outdated software to view sensitive files, they introduce a potential vulnerability to your entire ecosystem. Require that all devices connecting to your business cloud have up-to-date operating systems and active antivirus software.
Remote Wipe Capabilities
Mobile devices are frequently lost or stolen, making them a significant point of failure. Use mobile device management (MDM) software to ensure you can remotely wipe company data from a device if it goes missing. Most enterprise cloud platforms provide these tools, which allow you to sever the connection between a lost phone and your business account instantly.
Auditing and Monitoring for Anomalies
You cannot protect what you do not track. Regularly review the activity logs provided by your cloud service to see if any accounts are showing suspicious behavior.
An unusual spike in file deletions or failed login attempts is often the first sign of a compromised account. Set up automated alerts to notify your IT lead whenever a sensitive file is shared externally or a user logs in from a new geographic location.
- Review administrative activity logs every week.
- Disable inactive user accounts promptly.
- Audit external sharing permissions quarterly.
- Update recovery email addresses for all key stakeholders.
- Test your backup restoration process once per year.
Securing Collaborations with External Partners
Working with outside contractors often requires you to grant them access to your internal cloud storage. This is a common vector for security breaches, as you have less control over their local device security.
Create a dedicated folder for external partners rather than adding them to your main company directory. This limits their visibility to only the files necessary for their specific contract.
The Role of Guest Access
Many cloud platforms provide a “guest” or “temporary” access role specifically for this purpose. These roles often come with built-in restrictions, such as preventing the user from downloading files or sharing them further.
Always use these restricted roles for third-party collaborators rather than full user accounts. When the project ends, delete the guest account immediately.
Frequently Asked Questions
How can I protect data that is stored in the cloud?
You can protect your data by enforcing multi-factor authentication, using strong encryption, and regularly auditing your account logs. Limiting user permissions and keeping your connected devices updated are also essential.
What types of files should I avoid uploading to cloud storage?
Avoid uploading executable files, scripts, or any documents containing sensitive passwords or unencrypted private keys. If you must store sensitive data, ensure the files themselves are encrypted before they are uploaded.
Can hackers access cloud storage?
Yes, hackers can access cloud storage if they gain your login credentials or exploit misconfigured sharing settings. Using MFA and strong, unique passwords significantly reduces the likelihood of an unauthorized person gaining access.
How to protect business data during a remote work transition?
Focus on securing the endpoints, such as employee laptops and phones, rather than just the cloud service itself. Ensure all remote connections are encrypted and use a virtual private network (VPN) if your team is accessing files over public Wi-Fi.
Is it safe to store highly confidential files on public cloud platforms?
It is safe if you use a provider that offers zero-knowledge encryption and granular access controls. You must also ensure that your internal security policies are strictly followed by everyone who has access to those specific files.
Final Thoughts on Cloud Security
Maintaining a secure digital environment is a continuous process of vigilance rather than a one-time setup. By implementing multi-factor authentication and strictly managing file permissions, you significantly reduce the risk of unauthorized access to your company’s information. Remember that your staff members are your most important security asset; keeping them informed about safe sharing practices is just as important as the software you deploy.
As you continue protecting Business Files When Using Cloud Storage, keep reviewing your access logs and updating your security protocols to stay ahead of potential threats. Start by auditing your current sharing settings today, and reach out to your IT team or service provider if you need help enabling advanced security features for your account.