Common Cybersecurity Risks Covered by Business Insurance
Understanding common Cybersecurity Risks Covered by Business Insurance is essential for any modern company operating in a digital environment. These policies provide a crucial safety net when unexpected technical failures, malicious hacks, or human errors lead to significant financial loss.
By identifying what your protection actually covers, you can move from a state of constant anxiety to one of informed operational readiness. This article breaks down the specific exposures that standard policies address, helping you navigate the complexities of digital protection so your business stays resilient regardless of the challenges you face.
Primary Financial Protections in Cyber Insurance
When a company experiences a data breach or a network outage, the financial impact often extends far beyond the immediate IT repair costs. Cyber insurance is designed to cover the heavy lifting associated with incident response, which includes forensic investigation, legal counsel, and public relations support. These policies act as a financial buffer, ensuring that your business does not collapse under the weight of sudden, unforeseen expenses.
Most standard policies cover the costs associated with notifying affected customers, which is a legal requirement in many jurisdictions following a data breach. You will also find that these agreements often pay for credit monitoring services for impacted individuals, helping to preserve your brand’s reputation. By covering these tangible expenses, insurers allow your team to focus on restoring operations rather than scrambling to find emergency funds.
Addressing Data Breach Liabilities
A data breach is perhaps the most frequent risk that small businesses face today. When sensitive customer information is leaked or stolen, the liability can be astronomical due to potential class-action lawsuits and regulatory fines. Insurance providers specifically tailor their language to address these liabilities, covering court costs, settlements, and even the regulatory penalties imposed by government agencies.
This coverage is vital because the legal environment regarding data privacy is constantly evolving. Even if you have strong security protocols, a single vulnerability in a third-party vendor can expose your records. Having a policy that covers these liabilities provides peace of mind, knowing that your company’s survival is not dependent on the outcome of a single lawsuit.
Business Interruption and Income Loss
Many owners overlook the fact that a cyberattack can effectively shut down their ability to generate revenue for days or even weeks. Ransomware attacks, for instance, often lock up critical systems, preventing you from processing transactions or accessing inventory databases. Business interruption coverage is a standard component of many modern policies, designed to replace the income you lose during these downtime periods.
These payments are calculated based on your historical revenue, helping to cover fixed costs like rent and payroll while your systems are offline. It is important to review the “waiting period” on your policy, as some insurers require a certain number of hours of downtime before the coverage kicks in. You can learn more about these specific criteria by reviewing the official resources on cyber planning provided by the Federal Communications Commission to ensure your internal recovery plans align with your insurance expectations.
Extortion and Ransomware Payments
The rise of sophisticated ransomware gangs has made extortion a common threat for businesses of all sizes. Attackers often demand payment in cryptocurrency to provide a decryption key or to prevent the public release of stolen data. While the decision to pay a ransom is complex and often debated, many cyber insurance policies include provisions for extortion expenses.
These provisions can cover the cost of the ransom itself, as well as the fees for professional negotiators who specialize in communicating with threat actors. This ensures that you have access to expert guidance during what is often the most stressful moment in a company’s history. By outsourcing this expertise, you avoid making impulsive decisions that could worsen the situation or violate legal compliance requirements.
Regulatory Fines and Legal Costs
Governments worldwide are implementing stricter data protection laws, such as the GDPR in Europe or the CCPA in California. Failing to comply with these regulations after a security event can lead to massive fines that can easily bankrupt a small enterprise. Cyber insurance policies are increasingly including specific riders for regulatory defense and the resulting financial penalties.
These policies cover the legal fees required to defend your business during a government investigation. They also assist with the costs of providing mandatory notifications to regulators and affected parties. Without this protection, the administrative burden of a single incident could consume your entire annual budget.
Social Engineering and Phishing Risks
Human error remains one of the most common Cybersecurity Risks Covered by Business Insurance. Employees are often the target of sophisticated phishing campaigns designed to trick them into transferring funds or revealing sensitive credentials. Social engineering coverage is now a standard, yet critical, addition to many commercial policies.
This coverage protects your business against the financial loss resulting from fraudulent instructions or unauthorized fund transfers. It is a distinct type of risk because it involves deception rather than a direct technical breach of your firewall. Having this specific protection ensures that your company is covered even when a well-meaning employee makes a mistake that leads to a financial loss.
Summary of Common Risks and Coverage
To clarify how these protections work, it is helpful to look at the relationship between the type of threat and the specific coverage provided by a standard policy. The following table illustrates how different common cybersecurity risks are addressed by insurance agreements.
| Risk Type | Primary Insurance Coverage | Financial Impact Area |
|---|---|---|
| Data Breach | Privacy Liability | Legal fees, settlements, and fines |
| Ransomware | Extortion Coverage | Ransom payments and negotiation fees |
| Network Outage | Business Interruption | Lost revenue and operating expenses |
| Phishing Fraud | Social Engineering | Direct theft of company funds |
What Is Typically Excluded
While insurance provides a robust safety net, it is not a cure-all for every possible scenario. Most policies contain specific exclusions, such as losses resulting from a company’s failure to maintain basic security updates or known vulnerabilities. You must understand these boundaries to maintain your eligibility for claims.
- Losses caused by intentional, criminal acts by the business owner.
- Costs associated with upgrading or improving your existing hardware or software.
- Loss of intellectual property or trade secrets, unless specifically endorsed.
- Damages occurring before the policy’s retroactive date.
- Bodily injury or property damage resulting from a cyber event.
Frequently Asked Questions
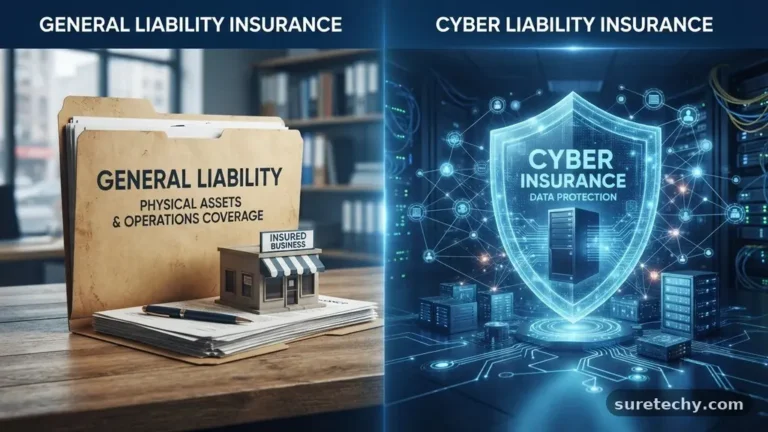
Does my general liability policy cover cyber attacks?
In most cases, no. General liability insurance typically covers physical property damage and bodily injury, not digital assets or data breaches. You almost always need a separate cyber insurance policy to handle these specific electronic risks.
How are premiums calculated for cyber insurance?
Insurers look at your industry, your annual revenue, and the amount of sensitive data you handle. They also evaluate your security posture, such as your use of multi-factor authentication and regular employee training, to determine your risk level.
What if I am a very small business?
Small businesses are often primary targets because they tend to have less sophisticated security than large corporations. Many insurers now offer “package” policies designed specifically for smaller firms that are much more affordable than custom enterprise solutions.
Is the cost of notifying customers covered?
Yes, most cyber liability policies include coverage for “event management,” which pays for the costs of notifying customers, setting up call centers, and providing identity theft protection for the victims of a breach.
Building Resilience
Navigating common Cybersecurity Risks Covered by Business Insurance is a foundational step in protecting your company’s future. While these policies are designed to handle the aftermath of an incident, they work best when paired with a strong internal security culture. By combining insurance protection with proactive measures like regular software patching and staff education, you create a layered defense that is difficult for attackers to penetrate.
Remember that insurance is a tool for recovery, not a replacement for security. Review your policy annually to ensure that your coverage limits match the growing value of your digital assets.
Taking these steps ensures that your business remains competitive and secure in an unpredictable digital landscape. If you have questions about your specific needs, reaching out to a qualified broker can help you tailor a plan that fits your unique operational reality.